Shivalik Bank.
Banking journeys connected.
Designed and developed.
Anviam developed the banking application from scratch, from design through PHP/Laravel and React.js development, with MySQL, AWS Lambda, two-factor authentication and role-based access.
From customer intent
to connected banking workflows.
- PHP / Laravel
- React.js frontend
- MySQL
- AWS & Lambda
Conceptual workflow illustration · Not a product screenshot
From Application Design to Connected Banking Workflows
- The productA banking application within a wider digital-services ecosystem.
- Anviam's contributionLaravel, React, MySQL, AWS Lambda, 2FA and role-based access, from design to development.
- The purposeConnect banking journeys with defined application and access workflows.
A Banking Application Connecting Design, Services and Access
A banking application developed from scratch, from design through development, using PHP/Laravel, React.js, MySQL, AWS and AWS Lambda, with two-factor authentication and role-based access.
Product Context
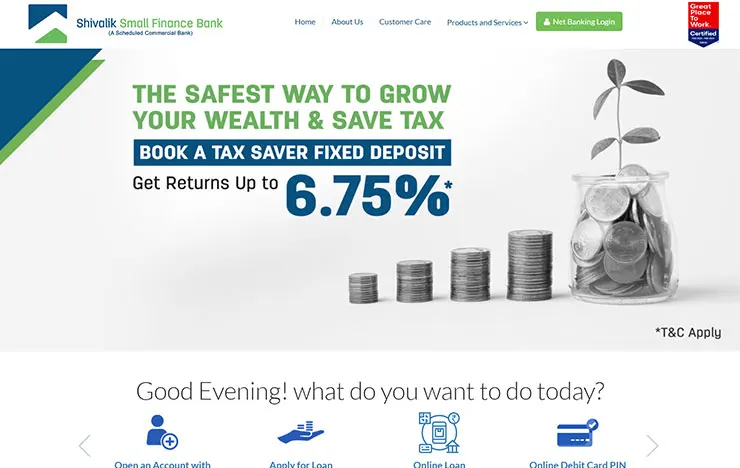
Shivalik Bank's public website presents banking products and digital-service entry points. This case study does not attribute the bank's core ledger, payment rails, every portal or mobile app to the engagement.
Users and Responsibilities
Customers need clear journeys and understandable request status; staff and administrative roles need appropriate authority. Public information and authenticated activity stay clearly distinct.
Connecting a Usable Banking Experience With Controlled Access
Relevant product and engineering requirements, not a reconstructed incident history.
Clear Customer Service Journeys
Users understand the chosen product, the information required, and whether they are making an enquiry, starting an application or entering an authenticated service.
Authentication and Recovery
Two-factor authentication needs clear challenge, expiry and recovery behaviour. Signing in and being authorised for a sensitive action are separate concerns.
Role Boundaries Across the Application
Permissions align with backend actions and record access, rather than depending on hidden interface controls.
Reliable Request and Cloud States
Asynchronous work, external responses and retries are handled explicitly. A submitted request is never shown as a completed banking outcome without confirmation.
Design to Banking-Application Development
Stack and responsibilities supplied directly for this case study.
Design and Development
From application design through development, built from scratch.
PHP / Laravel and React.js
A Laravel backend with a React.js frontend.
MySQL, AWS and Lambda
MySQL for application data, with AWS and AWS Lambda in the stack.
2FA and Role-Based Access
Two-factor authentication and role-based access across the application.
Figma files, framework versions, API contracts, database schema, AWS services beyond Lambda and the role matrix were not supplied and are not inferred.
Customer Banking Context With Confirmed Application Foundations
Public banking services are product context; their full implementation is not attributed to Anviam without additional evidence.
Account and Deposit Discovery
Public pages present savings and current accounts and deposit products.
Loan Information and Enquiries
Loan categories and application entry points on the public site.
Retail and Corporate Access
Links to separate authenticated retail and corporate banking services.
Account Overview Context
The retail page describes an overview of accounts, deposits and loans.
Transfers and Beneficiaries
Public retail features include NEFT/RTGS/IMPS transfers and beneficiary management.
Deposit and Service Controls
Deposit management, card controls and cheque services, as advertised.
Customer Support Paths
Contact, complaints and reporting of unauthorised transactions.
Two-Factor Authentication
Confirmed project scope; exact factors and workflows were not inspected.
Role-Based Cloud Application
Confirmed scope: role-based access with React/Laravel, MySQL, AWS and Lambda.
Choose the Service. Verify Access. Review the Outcome.
A conceptual journey based on public banking context and the supplied authentication scope. No account, identity document, payment or customer record was accessed.
Find the relevant service
Start with the product or customer-service route for the task.
Review requirements
Read the available information before applying or signing in.
Enter the application
Use the intended banking entry point for the service.
Complete authentication
Login and second-factor process where required.
Access permitted functions
Actions shown according to role and authority.
Provide and validate
An incomplete form is distinct from an accepted request.
Review before submission
Sensitive or irreversible actions are presented clearly.
Confirm status
Submitted, pending, failed and completed stay distinct.
Close or seek support
End the session or get help without exposing sensitive data.
Application, Identity and Cloud Responsibilities Working Together
Engineering considerations for the supplied stack, not an inspected architecture or audit report.
Laravel and React service boundaries
Validation, permissions and request/response states defined consistently across frontend and backend. Core-banking connectors are not inferred from a product link.
Two-factor lifecycle
Challenge validity, throttling, enrolment and recovery reviewed, with factor independence and sensitive-action requirements evaluated rather than treating every OTP screen as equivalent.
Backend role enforcement
An explicit permission matrix with server-side checks, reviewing privileged access and segregation of duties against the intended business workflow.
MySQL integrity and access
Record relationships, update rules and restricted queries defined. No ledger design, reconciliation engine or transaction-volume benchmark is asserted.
AWS Lambda execution boundaries
Idempotency, retries, timeouts and secrets planned for the actual Lambda task. A listed cloud component does not establish a particular event-driven architecture.
Monitoring and recovery
Logging, alerting, rollback and recovery criteria agreed, with sensitive data minimised in operational output. No uptime or disaster-recovery result is claimed.
A Design-to-Development Foundation for Banking Workflows
The confirmed scope joins application design, Laravel/React development, MySQL, AWS/Lambda and access-control implementation in one engagement.
Useful measures include authentication failures, permission test coverage, request completion, validation errors and recoverability. No customer-growth, financial saving, transaction-speed or security-incident result is claimed.
Connected Delivery Responsibility
User-facing behaviour and the supporting application and cloud components, delivered together.
Banking Governance, Privacy and Evidence-Based Assurance
Applicability must be assessed for the actual processing. No compliance audit or certification evidence was provided, and none is claimed.
Indian Banking IT Governance
Applicable RBI IT governance, risk, controls, assurance and outsourcing requirements, assessed against the regulated entity and service scope.
Indian Personal-Data Requirements
The DPDP Act and Rules, including commencement dates: notices, processing, access, retention and provider responsibilities.
GDPR Where Applicable
Relevance depends on territorial and processing scope; an Indian bank website alone does not establish it.
HIPAA Only Where Applicable
HIPAA concerns covered entities and protected health information; a banking application is not HIPAA-regulated by default.
Authentication and Authorisation Evidence
2FA and role-based access are confirmed scope; effectiveness needs implementation review and negative testing.
Payments and Cloud Responsibilities
Determined from actual integrations. No PCI DSS validation, core-banking approval or regulatory endorsement is claimed.
Why Anviam for Your Banking Application?
Bring application design, full-stack implementation and access requirements together around defined banking workflows. See our Laravel development and cybersecurity services.
Talk Through Your Project- Design through development: implementation, not an isolated visual refresh.
- Laravel backend experience for application rules, validation and service behaviour.
- React.js frontend delivery for clear journeys, statuses and review steps.
- MySQL application data without assuming a core ledger or proprietary bank schema.
- AWS and Lambda experience tied to the actual processing, recovery and operations.
- Two-factor authentication covering enrolment, expiry and recovery.
- Role-based access as explicit permissions with testable backend enforcement.
- Banking-context product decisions separating discovery, applications and authenticated activity.
- Evidence-led delivery criteria before publishing security, compliance or business results.
Sources and evidence
Development scope supplied by Anviam. Public website and retail-banking information reviewed 21 October 2026; current services are context, not proof that every bank system was delivered by Anviam. No authenticated application, banking transaction, source code or security assessment was accessed. HIPAA/GDPR in the brief does not establish universal applicability or certification.