CloudXDN.
Security meets AI.
Built for the cloud.
Anviam developed CloudXDN from scratch, connecting an Angular.js frontend and Java/Spring Boot backend with an AI chatbot, cloud copilot, agent workflows, LLMs, RAG and prompt engineering.
From security findings
to reviewed action.
- SaaS from scratch
- Angular.js frontend
- Java / Spring Boot
- AI agents & LLM/RAG
Conceptual workflow illustration · Not a product screenshot
From Cloud Context to AI-Assisted Security Workflows
- The productAn AI-powered security policy and compliance platform.
- Anviam's contributionAngular.js, Java/Spring Boot and AI application development, built from scratch.
- The purposeConnect policy context, findings and reviewed next actions.
Security Policy and Compliance in an AI-Assisted SaaS Workspace
Anviam developed CloudXDN from scratch with an Angular.js frontend and Java/Spring Boot backend. The scope includes an AI chatbot, cloud copilot, AI agents, LLMs, RAG and prompt engineering.
Product Context
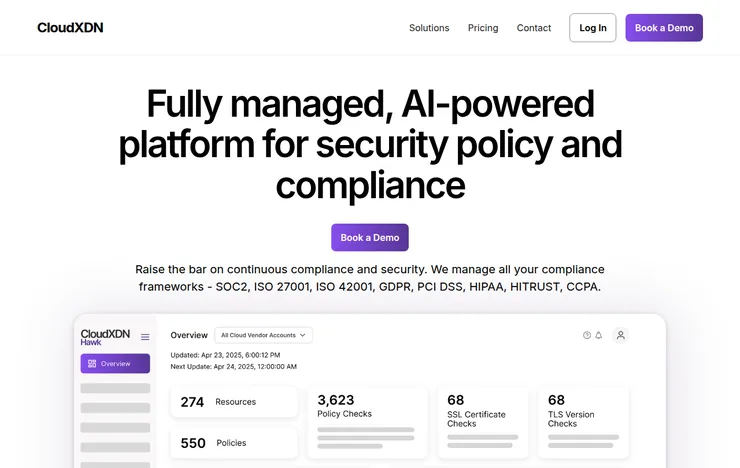
CloudXDN presents a managed cloud-security and compliance platform. Its public description establishes the feature context; authenticated workflows and individual controls were not inspected.
Users and Responsibilities
Cloud operators, security teams and compliance stakeholders need to understand findings, policy context and the next action. AI assistance stays distinguishable from verified evidence and authorised changes.
Making Security Findings Understandable and Actionable
Engineering requirements relevant to the product, not a reconstructed history of incidents.
Findings With Context
A violation needs resource context, policy meaning and freshness information, so users can investigate rather than treat a dashboard count as a complete compliance assessment.
Grounded AI Guidance
Security prompts and retrieved context can contain sensitive data or untrusted instructions. The application needs defined context boundaries and evaluation of unsupported recommendations.
Remediation With Explicit Authority
A recommended change and an executed change are different states. Agent responsibilities, permissions and review gates need deliberate definition.
Evidence Across Frameworks
Mapping a policy to a framework can assist review, but does not establish that every requirement is implemented or that an audit has passed.
Angular.js, Spring Boot and AI, Built From Scratch
The following scope was supplied directly for this case study.
Development From Scratch
Developed the SaaS application from scratch across frontend and backend.
Angular.js Frontend
Built the Angular.js frontend for findings, policies and AI-assisted review.
Java / Spring Boot Backend
Developed backend functionality with Java and Spring Boot.
LLM, RAG and AI Workflows
Implemented the AI chatbot, cloud copilot, agents, LLM/RAG and prompt engineering.
Policy Visibility, Cloud Assessment and AI Assistance
Capabilities described on the public website. Availability depends on the product plan and configuration.
Policies and Findings
- Custom security policies
- Visibility into violations
- Continuous environment auditing
Frameworks and Code
- Policy-to-framework mapping
- Terraform code scanning
- GitHub integration
AI Assistance
- AI chatbot queries with graph outputs
- GenAI policy copilot
- AI-recommended remediation
- Agents, LLMs, RAG and prompt engineering (Anviam scope)
Published plans distinguish single-account/region and multi-account/region use. In-app agent tools were not inspected.
Assess the Environment. Understand the Findings. Review the Response.
A product-level journey inferred from public capabilities and the AI scope. Exact screens, scan triggers and execution rights were not inspected.
Set the environment scope
Select the accounts and regions available under the configured plan.
Set policy context
Identify the policies and framework mappings relevant to the review.
Assess environment or code
Run the available assessment; Terraform scanning is a separate capability.
Inspect findings
Review resource context and violations rather than a headline count alone.
Consult the AI copilot
Ask for relevant assistance within the permitted context.
Review drafts or remediation
Check AI suggestions against evidence, requirements and operational constraints.
Authorise the next action
Route proposed changes through permissions and review. Autonomous execution is not claimed.
Reassess the result
Confirm the state after an approved action.
Retain review evidence
Keep a record of findings, decisions and remaining exceptions.
LLM and RAG Workflows Connected to a Security Product
Engineering considerations relevant to the delivery scope, rather than an inspected internal architecture.
RAG context and access boundaries
Retrieve only context the user is permitted to access, and preserve source identity and freshness. Relevant retrieval does not guarantee a correct answer.
Prompt engineering and untrusted input
Separate instructions from retrieved data and resource descriptions, and assess prompt-injection scenarios and unintended disclosure across context boundaries.
AI agent permissions
Define permitted tools, read/write scope, approval gates and failure behaviour. A chatbot response does not establish authority to alter cloud infrastructure.
Spring Boot service contracts
Keep policy, finding and remediation states explicit across backend operations, with defined validation and error handling.
Frontend review experience
Use the Angular interface to distinguish evidence, generated guidance, review decisions and action status, keeping exceptions and uncertainty visible.
Quality and operational evaluation
Evaluate unsupported claims, retrieval relevance, permission failures and task completion alongside latency. No benchmark or model accuracy result is asserted.
A Full-Stack Foundation for AI-Assisted Security Workflows
The engagement joins frontend, backend and AI implementation in a SaaS product built from scratch.
Useful measures include finding triage time, mapping coverage, false-positive review, AI factual consistency and approved-action success. No compliance pass rate, incident reduction, cost saving or certification result is claimed.
Connected Application Capability
A cloud-security interface brought together with Java/Spring Boot services and LLM/RAG workflows.
Framework Support With Explicit Evidence Boundaries
The project followed HIPAA/GDPR compliance requirements. No independent compliance audit, certification or legal assessment is claimed.
GDPR / UK GDPR Where Applicable
Personal-data purposes, lawful processing, transparency, access, retention, processors and transfers, with accountable governance for AI processing.
HIPAA for Applicable Deployments
Where protected health information is involved, assess the actual relationship, safeguards and business associate arrangements.
Advertised Framework Coverage
SOC 2, ISO 27001, ISO 42001, GDPR, PCI DSS, HIPAA, HITRUST and CCPA are advertised coverage areas, not certifications held.
Cloud Credentials and Least Privilege
Environment access, credential storage, segregation of duties and revocation. Deployed controls were not audited.
AI Data Handling and Governance
Define what enters prompts, retrieval context and logs, whether providers retain it, and how access is controlled.
Evidence and Change Accountability
Preserve findings, review decisions and authorised changes under the retention policy. A generated policy is not a completed external audit.
Why Anviam for Your Cloud-Security AI Platform?
Bring application engineering and AI integration together around policies, findings and reviewed operational decisions.
Talk Through Your Project- Developed from scratch: a complete frontend/backend application, not an isolated AI demo.
- Angular frontend experience for review interfaces, findings and action states.
- Java / Spring Boot backend services connected to the product experience.
- AI chatbot and copilot delivery inside a user-facing application.
- LLM and RAG implementation with permitted retrieval context and grounded responses.
- Prompt engineering with clear task structure, source boundaries and output expectations.
- AI agent workflows with tool permissions, review gates and defined responsibilities.
- Compliance-aware requirements translated into reviewable product and data-handling decisions.
Sources and evidence
Scope supplied by Anviam. Public features and plan descriptions may reflect later releases. Authenticated screens, source code, models, tool permissions and controls were not inspected. Framework coverage does not assert certification.